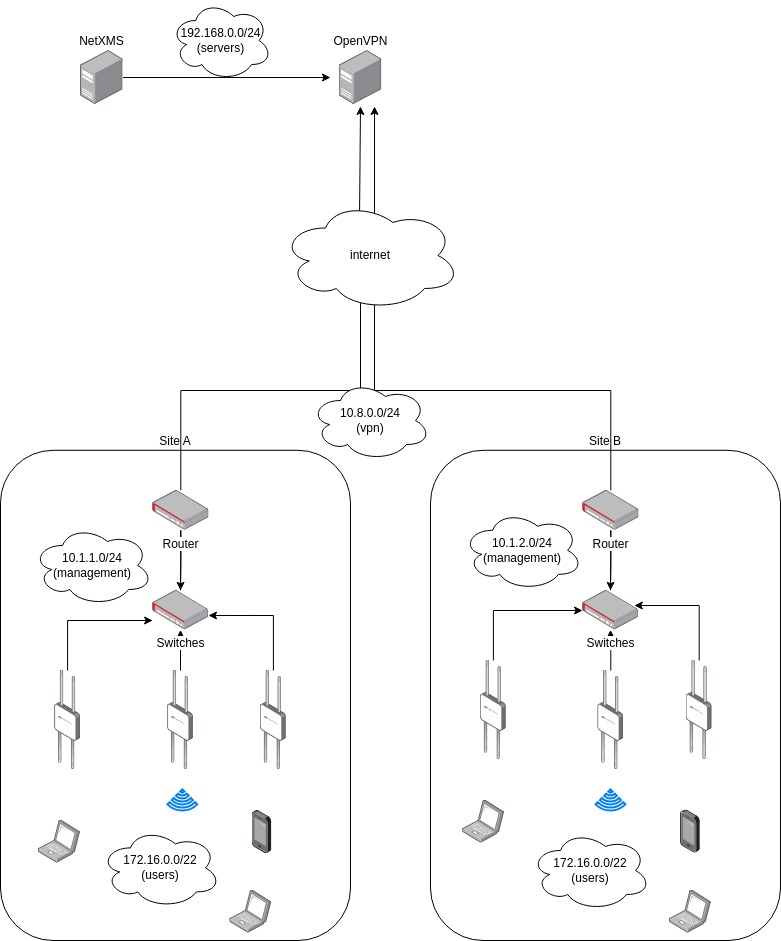
There is my agent config, ping/ssh subagents and enableProxy/enableSNMPProxy were already on:
LogFile={stdout} # or file name, might want to mount a volume for this
DebugLevel=0 # 0-9
MasterServers=0.0.0.0/0 #list of NetXMS servers with full access
#ControlServers=… # list of NetXMS servers with read+execute actions access
#Servers=… # list of NetXMS servers with read-only access
SubAgent = linux.nsm
SubAgent = ecs.nsm
SubAgent = filemgr.nsm
SubAgent = ping.nsm
SubAgent = logwatch.nsm
SubAgent = mqtt.nsm
SubAgent = netsvc.nsm
SubAgent = portcheck.nsm
SubAgent = ssh.nsm
SubAgent = mqtt.nsm
#SubAgent = winperf.nsm
#SubAgent = wmi.nsm
#SubAgent = ups.nsm
EnableProxy = yes
EnableSNMPProxy = yes
EnableSNMPTrapProxy = yes
EnableSyslogProxy = yes
EnableTCPProxy = yes
You're right, I didn't need the 161 NAT rule, I've dropped it.
But still, I've tried both things:
- creating an icmp.ping metric to a node that container can actually ping => the metric status is in ERROR state
- adding manually a node, put it in the zone, then defining my mikrotik container agent node as a proxy for ICMP and SNMP => in the status poll logs I can see "Starting ICMP ping via proxy", followed by "Node is still unreachable"