
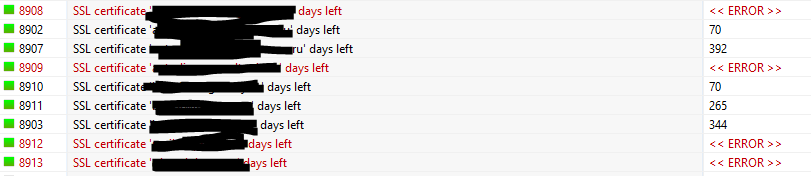
После перехода с 3.9 на 4.3.1 плохо работает проверка сертификатов
-
-
На 7 уровне дебага на агенте видны подробности, там openssl вызывается:
2023.02.15 00:46:09.805 *D* [comm.cs.98 ] Requesting metric "HTTPS.CertificateExpireDate(host)"
2023.02.15 00:46:09.805 *D* [comm.cs.98 ] H_ExternalMetric called for "HTTPS.CertificateExpireDate(host)" "openssl s_client -showcerts -servername $1 -connect $1:443 </dev/null 2>/dev/null | openssl x509 -inform pem -noout -enddate | cut -d = -f 2"
2023.02.15 00:46:09.805 *D* [exec ] RunExternal called for "HTTPS.CertificateExpireDate(host)" "openssl s_client -showcerts -servername $1 -connect $1:443 </dev/null 2>/dev/null | openssl x509 -inform pem -noout -enddate | cut -d = -f 2"
2023.02.15 00:46:09.806 *D* [exec ] RunExternal: command line is "openssl s_client -showcerts -servername host -connect host:443 </dev/null 2>/dev/null | openssl x509 -inform pem -noout -enddate | cut -d = -f 2"
2023.02.15 00:46:09.809 *D* [procexec ] ProcessExecutor::execute(): process "openssl s_client -showcerts -servername host -connect host:443 </dev/null 2>/dev/null | openssl x509 -inform pem -noout -enddate | cut -d = -f 2" started
2023.02.15 00:46:09.827 *D* [procexec ] ProcessExecutor::readOutput(): stopped on read (rc=0 err=Success)
2023.02.15 00:46:09.827 *D* [comm.cs.98 ] GetMetricValue("HTTPS.CertificateExpireDate(host)"): 0 (SUCCESS) value = "unable to load certificate"Можно агента оставить с дебагом на 7 уровне, там будет видно что возвращается. Или просто погонять на эту команду на системе.
-
Windows Server 2019
дебаг агента 9 уровень, агент 4.3.1
включен субагент SubAgent = portcheck.nsm
вызова openssl не видно2023.02.15 08:45:36.170 *D* [comm.cs.1 ] Requesting metric "TLS.Certificate.ExpiresIn(mail. ###,443)"
2023.02.15 08:45:36.201 *D* [netsvc ] NetConnectTCP(mail. ###.ru:443): connect failed (timeout 30 ms)
2023.02.15 08:45:36.201 *D* [comm.cs.1 ] GetMetricValue("TLS.Certificate.ExpiresIn(mail.###.ru,443)"): 500 (INTERNAL_ERROR) value = ""Нет там таймаута, валится сразу
Вызов openssl с того же сервера нормально возвращает ответ
openssl s_client -showcerts -servername mail.###.ru -connect mail.###.ru:443P.S. Кстати, агент мне не предлагает параметр HTTPS.CertificateExpireDate, как в примере.
-
Да, HTTPS.CertificateExpireDate - это я фигню написал - на системе где я смотрел был настроен такой ExternalParameter.
А с TLS.Certificate.ExpiresIn есть ошибка в коде - там таумаут по умолчанию должен был быть 30 сек, а получился 30 мс. Будет поправлено в следующем патч релизе.
На сейчас можно сделать так:
TLS.Certificate.ExpiresIn(mail.###.ru,443,,timeout=30000)
Только после патч релиза нужно будет это убрать или заменить на timeout=30, иначе таймаут станет 30 тысяч секунд -
Таймаут все-таки будет задаваться в миллисекундах, так что TLS.Certificate.ExpiresIn(mail.###.ru,443,,timeout=30000) может оставаться и в дальнейшем
-
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login