
Syslog Parser
-
Hi,
i want to parse syslog from Cisco devices.
For Example:
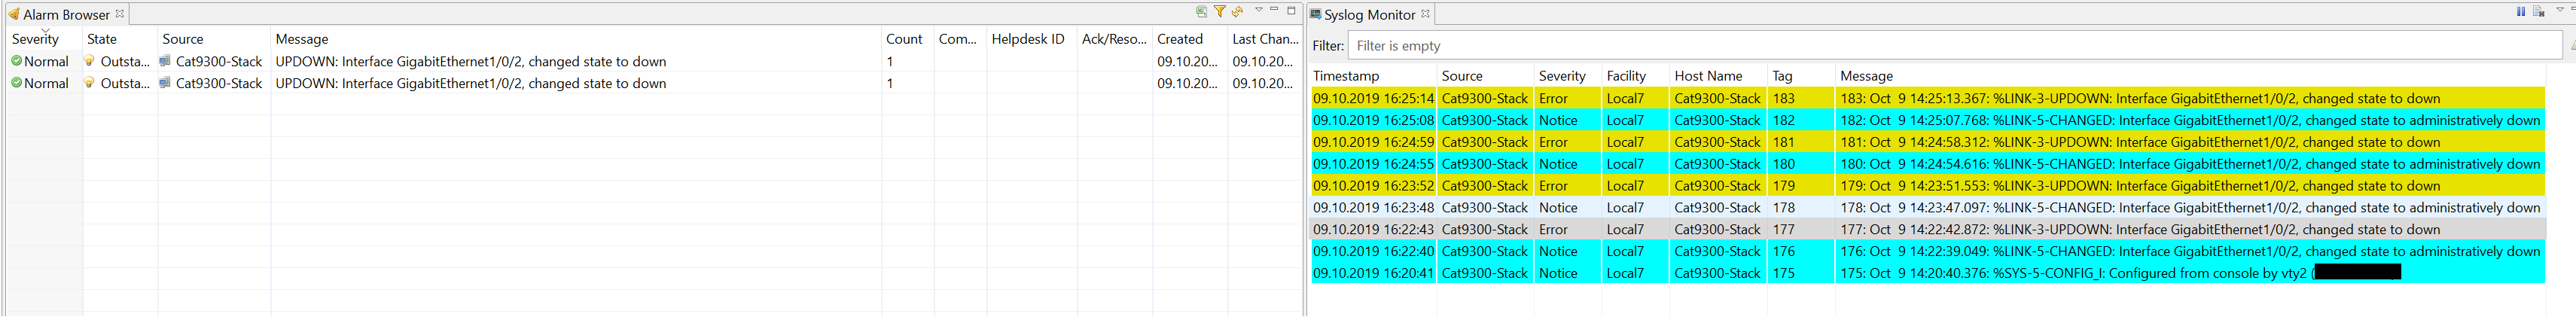
I got a syslog message in the syslog monitor like that:
09.10.2019 16:22:43 Cat9300-Stack Error Local7 Cat9300-Stack 177 177: Oct 9 14:22:42.872: %LINK-3-UPDOWN: Interface GigabitEthernet1/0/2, changed state to downThen i want that a Event creates a message in my alarm browser.
So far so good. That works already but i want to that in the alarm browser the field count increments.Any ideas how i can do that?
Best regards
-
If the same event on the same device triggers the same Alarm key, then the counter should increase rather than a second alarm being created.
The Alarm key is set as part of the Event Processing Policy.You can also check the Alarm Log (not the Alarm Browser) to see the exact Keys for the two alarms in your screenshot, which might help you in determining where things are going wrong.
-
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login