
Web API Authentication Question: Bearer Token vs. Session-Id
-
I'm facing an issue with the Web API authentication on my setup (Ubuntu server with Tomcat 9).
I can authenticate and make API calls successfully when using a temporary session-id
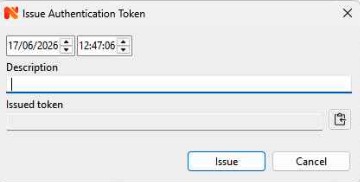
obtained via the login endpoint. However, when I try to use a permanent API token (generated in the Management Console), I consistently get I consistently get error: 46 (NXSL_CLASS_NOT_FOUND)
My main question is: should authentication with permanent API tokens (Bearer Tokens) work as expected? Or for automation scripts, is the correct approach to always fetch a temporary Session-Id first?

-
Tokens generated from Management Console are intended for different things - currently I think only for publishing network maps.
So yes, current way it to get temporarily session id.UPD: actually permanent tokens are supported in the new API - the one that is server module and is currently under development. But not in the old one.
Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login