
Not able to configure DCI TABLE in new version
-
Hello,
I want to user <<TABLE>> in data collection for radius accounting but it is showing error unsupported.
how to use it?Regards,
Dushyant Dave -
I am using version 1.2.6
and in DCI TABLE using accounting server .1.3.6.1.2.1.67.2.1.1.1 -
-
Dear Jorg,
I want snmpwalk result in NetXMS Table
My radius server SNMP service is working on 1161 port
I am able to do snmpwalk -v1 -cpublic 10.106.1.254:1161 .1.3.6.1.2.1.67.1.1.1.1.15.1
I want all the radiusAuthClientEntry - .1.3.6.1.2.1.67.1.1.1.1.15.1 tree
in the NetXMS Tablebut it is showing unsupported.
please help.Thanks & Regards,
Dushyant Dave -
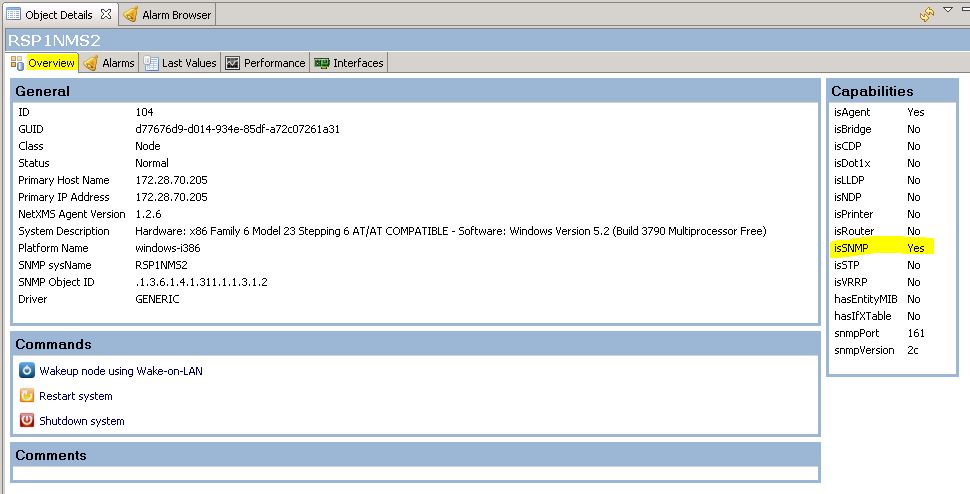
Do you have SNMP settings set correctly on the node? Does node has "isSNMP" set to yes in capabilities?
Best regards,
Victor -
my snmpd configuration is as below:
trapcommunity public
group MyRWGroup v1 local
group MyRWGroup v2c local
group MyROGroup v1 mynetwork
group MyROGroup v2c mynetwork
view all included .1 80
access MyROGroup "" any noauth exact all none none
access MyRWGroup "" any noauth exact all all nonealso find attached scrrenshot , I didn't found any issnmp option in the node.
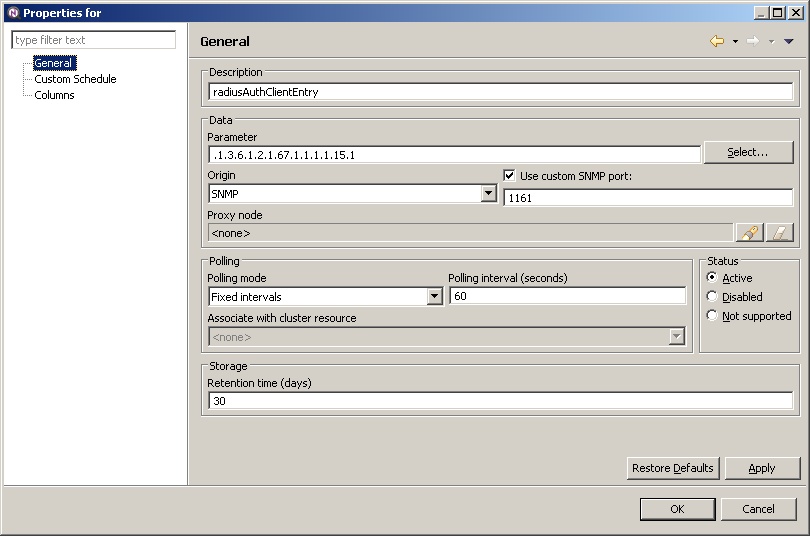
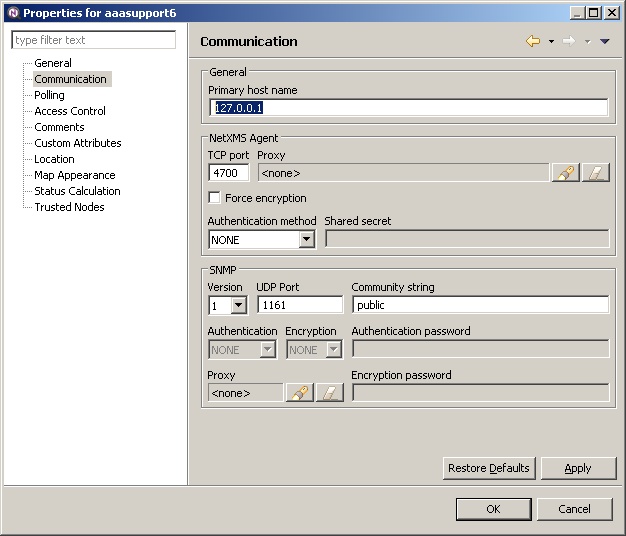
-
-
isSNMP is showing yes, please find the error screenshot.
I am using RHEL 5.3 32bit
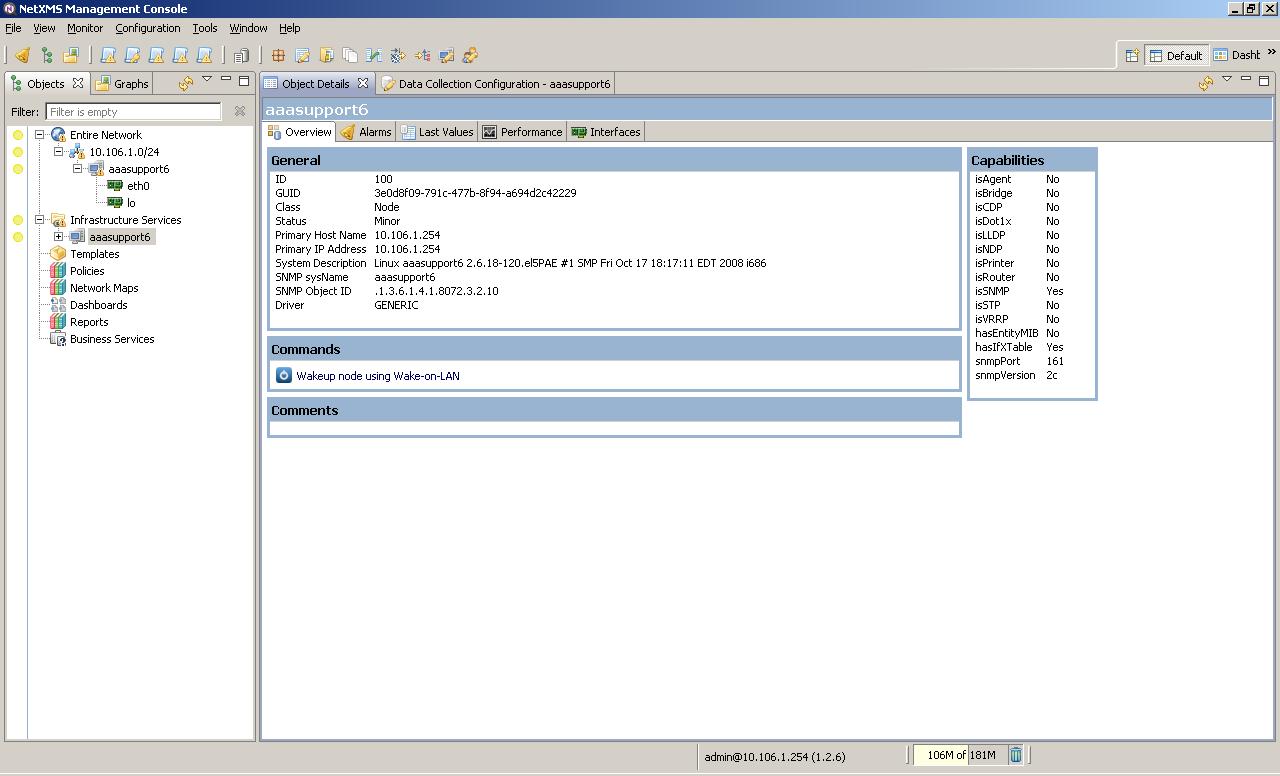
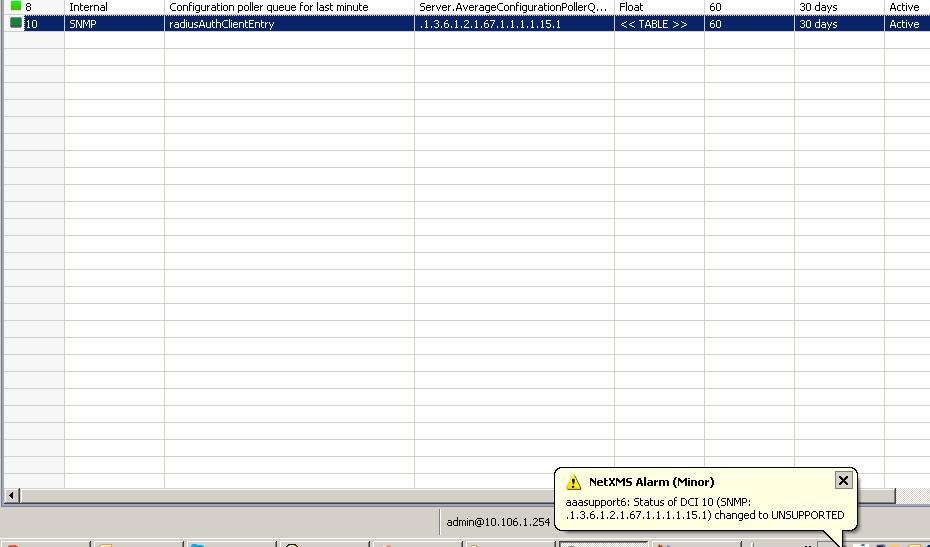
-
Hi,
I think you mixed up some thinks in your configuration.
You test the access with snmpwalk directly on the machine and uses the community "public" and port 1161.
But in your posted snmpd.conf there is not such a community (I guess it's the conf from your radius server).
Also I miss the mapping of the community name (COMMUNITY) into a security name.Example:
# sec.name source community
com2sec local localhost public
com2sec mynetwork 10.1.1.0/28 publicAfter that you normally map the security names into group names:
# sec.model sec.name
group MyRWGroup v1 local
group MyRWGroup v2c local
group MyRWGroup usm local
group MyROGroup v1 mynetwork
group MyROGroup v2c mynetwork
group MyROGroup usm mynetworkThen you create a view or views like:
# incl/excl subtree
view all included .1
view sysView included systemAnd finally you grant the groups access to the views with different write permissions:
# context sec.model sec.level match read write notif
access MyROGroup "" any noauth exact system none none
access MyRWGroup "" any noauth exact all all noneI would suggest that you adjust your smnpd.conf accordingly.
-
Hello Joos68,
I have updated my snmpd.conf as mentioned but still I am getting DCI changed to UNSUPPORTED.
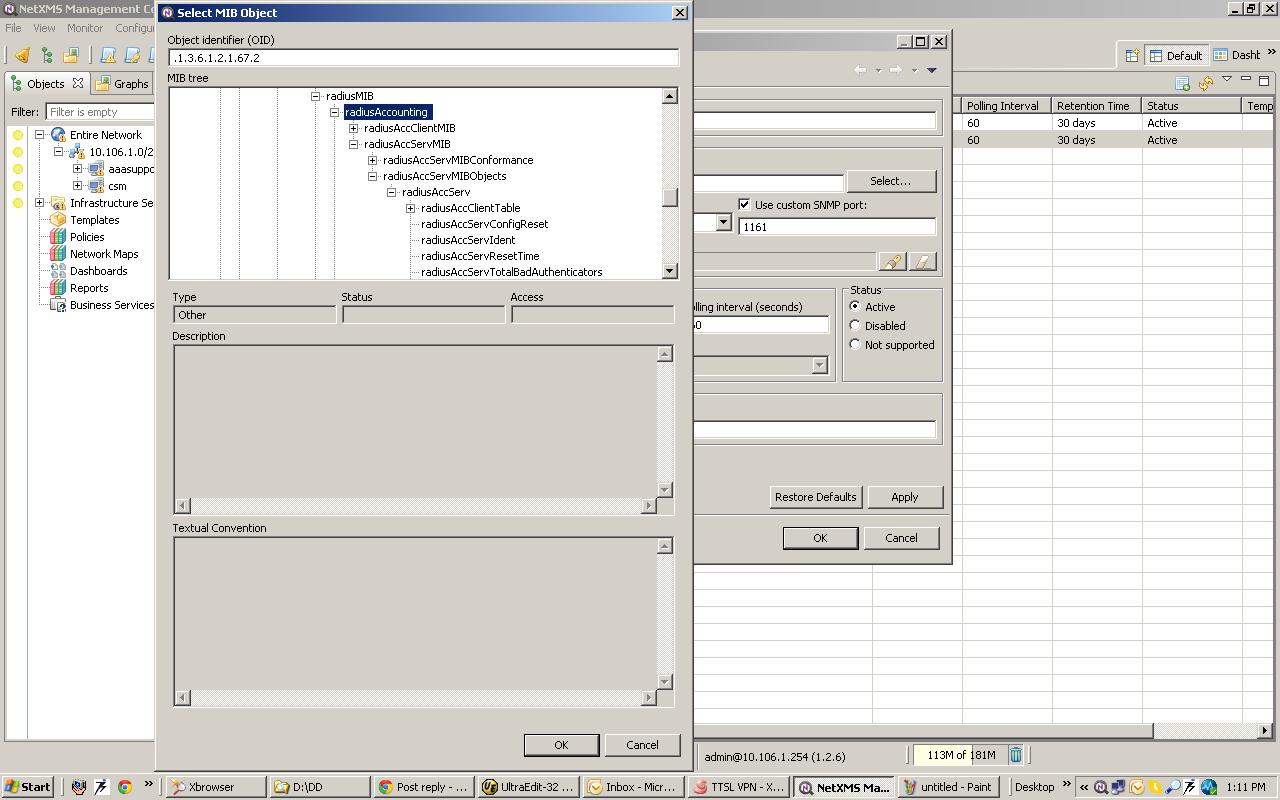
I have attached screenshot of radius mid tree, please guide me which tree I have to select for DCI Table
and I am using version 1.2.6 is it ok?

Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login